Most business owners picture cybercriminals as shadowy figures writing clever code to break through firewalls. In reality, the most successful attack technique right now doesn’t rely on clever code at all — it relies on asking politely. According to Microsoft’s own threat intelligence data, a scam called “ClickFix” was the single most common way attackers gained access to company systems last year, and it works by simply convincing someone to copy and paste a command into their own computer.
For small and medium businesses across Gippsland and regional Victoria, this matters enormously. ClickFix doesn’t need a technical vulnerability, an unpatched server, or an expensive exploit kit. It needs one distracted staff member and thirty seconds of their time. That’s a much lower bar than most cybersecurity advice assumes, and it’s exactly why this technique has spread so fast.
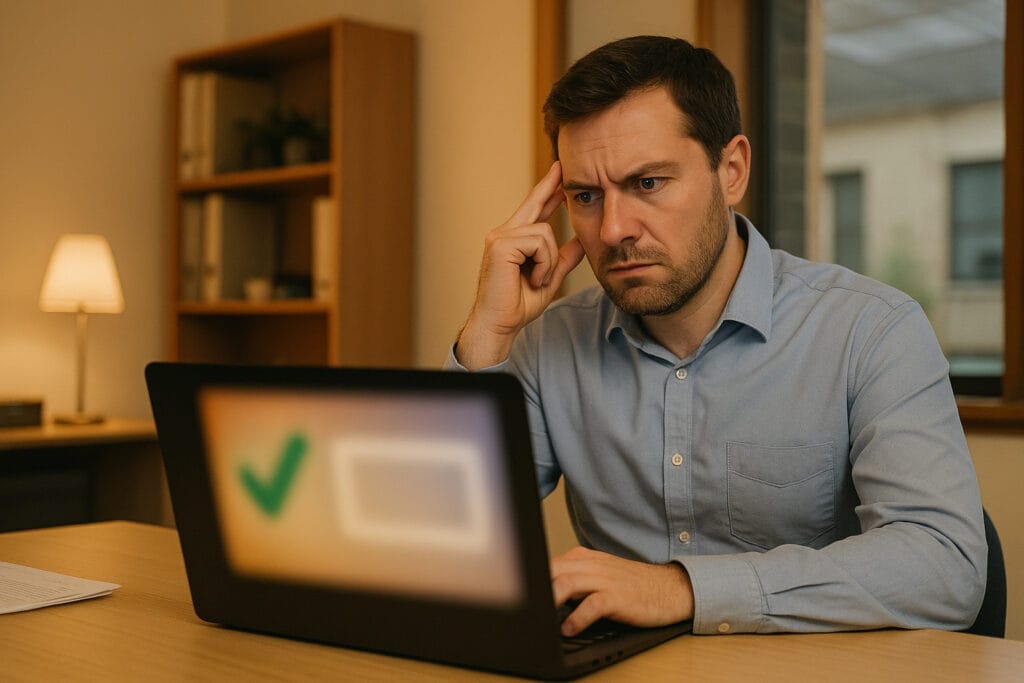
The trick usually starts with something that looks completely mundane: a pop-up on a website, or a link in an email, asking the visitor to “verify you are not a robot.” Instead of the familiar tick-box CAPTCHA most people are used to, the page displays instructions — something like “press Windows key + R, then paste and press Enter.”
What the victim doesn’t realise is that clicking the “verify” button has already copied a malicious command onto their clipboard. The instructions are simply talking them through pasting and running it themselves. Because the person is the one physically typing the keys and clicking “run,” many security tools don’t flag it as suspicious — it looks like normal user activity, not an attack.
Once run, that command can quietly install a remote access tool, a password stealer, or a backdoor that gives an attacker ongoing access to the computer and, from there, the wider business network.
As reported by The Hacker News, security researchers describe this shift as attackers moving away from chasing “better” or more sophisticated attacks and instead favouring ones that are cheap, repeatable, and reliable across thousands of targets. ClickFix fits that description perfectly. It doesn’t require a software bug that might get patched next week. It exploits a much more permanent weakness: human trust and habit.
It also thrives because it looks so ordinary. Staff members are trained to be wary of obvious phishing emails with poor spelling or strange attachments, but a fake “prove you’re human” check feels routine — something we all click through dozens of times a week without thinking. Attackers are deliberately hiding inside that everyday familiarity.
There’s a common assumption that a small accounting firm in Traralgon or a retailer in Warragul is too small to be worth an attacker’s time. Unfortunately, the opposite is true. Techniques like ClickFix are attractive to criminals precisely because they scale — the same fake verification page can be shown to thousands of visitors across the country simultaneously, with no extra effort required per victim. A business doesn’t need to be a specific target; it just needs one employee to land on the wrong page or click the wrong link.
Regional businesses are often particularly exposed because:
ClickFix pages are designed to feel legitimate, but there are some tell-tale signs staff can be trained to notice:
You don’t need an enterprise security budget to defend against this technique. Most of the effective countermeasures are about awareness and basic system hygiene rather than expensive tools.
The rise of ClickFix is a reminder that cybersecurity isn’t only about firewalls, patches, and antivirus subscriptions — it’s about the everyday decisions your staff make at their keyboards. Attackers have realised that a simple, repeatable trick that fools one person in a hundred is far more profitable than a sophisticated attack that only works on a handful of highly specific targets. For regional businesses without a dedicated IT security team watching every alert, building that awareness into daily habits is one of the most cost-effective defences available.
If you’re not sure whether your business is exposed to this kind of risk, Maximum IT Solutions offers a free security assessment for businesses across Gippsland and regional Victoria. We’ll review your current setup and flag anything that needs urgent attention — no obligation.
(+61) 0412 440 804